 Nocturn
Developer APIBeta
Nocturn Quality
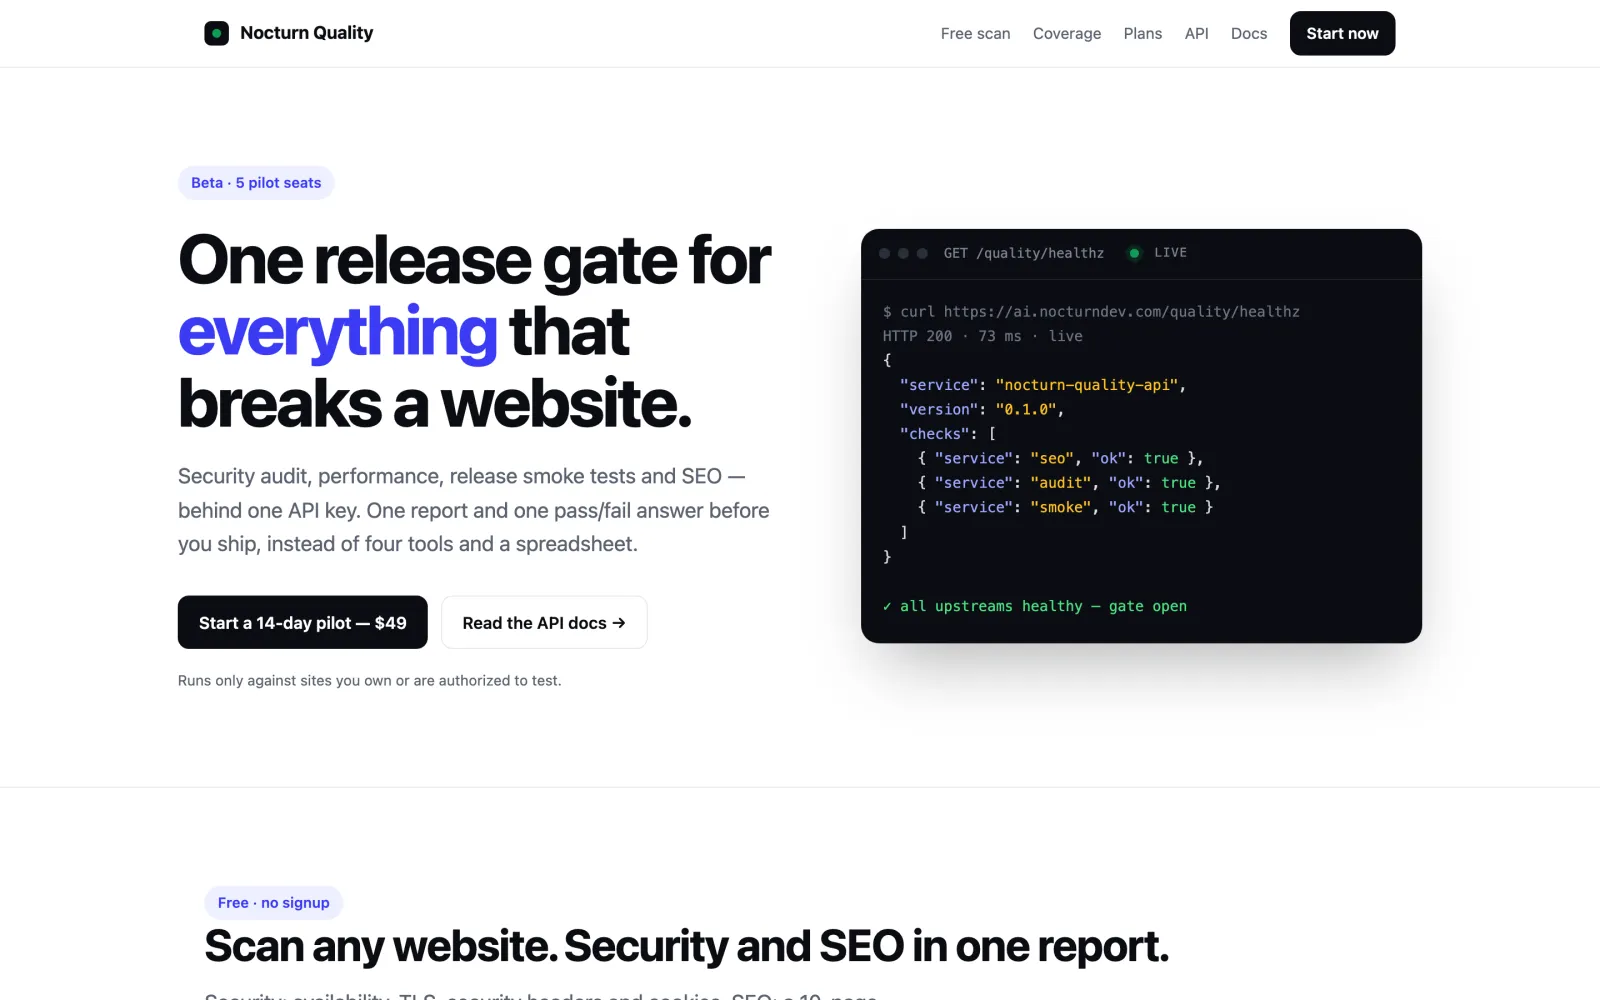
Four checks that usually live in four tools, each running as its own service behind a single gateway: one base URL, one key, one contract, and one answer to “is this release safe to ship?”
The problem
Teams run a security scanner, Lighthouse, an uptime service and an SEO crawler — four logins, four reports, and nobody whose job is to combine them before a Friday deploy. Regressions slip through the gaps between tools.
What we built
- API gateway in front of independent audit, smoke, performance and SEO services
- Free, no-signup passive scan on the public page
- OpenAPI reference, idempotent job submission and per-tenant keys
- Bilingual findings (English and Turkish) from the same rule set
Engineering notes
A public scanner that cannot be aimed inward
Accepting arbitrary URLs is an SSRF invitation. The scanner resolves DNS itself, rejects private and reserved ranges, connects only to the address it verified, re-checks every redirect hop and allows ports 80 and 443 only. Response bodies are capped.
Passive by default, verified for anything heavier
Anyone can run ordinary page requests — the same ones a browser or crawler makes. Load tests and source audits run only against targets the customer has proved they control.
Deploys that roll themselves back
Each service ships with a deploy script that verifies health after restart and restores the previous build automatically if the check fails.